REVIEWED 2026-09-08

The claims.
The code behind them.

Inspect what each component does, where the evidence lives, and what remains open.

How to read this page

This is a dated review of repository source, package metadata, and retrieved GitHub workflow results. Source was read at the commits below. Product tests were not executed during this audit; CI results are snapshots, not live monitors or independent assurance.

Execution kernel

gove-zone

Beta · release candidate

Release and source

PyPI lists 1.0.0rc2, uploaded August 23. The inspected monorepo uses a 1.0.0rc1 fallback. These are different artifacts; release reconciliation remains open.

Failed

Kernel test run failed

At the inspected monorepo commit, python-gove-zone failed its Python 3.11 test step; the Python 3.12 test job was cancelled. Packaging smoke and platform-lock jobs passed. No tests were rerun for this review.

Python policy library

ACGS-Lite

Beta

Release and source

Release 3.0.1 was published to PyPI on September 21 (following 3.0.0’s Z3 AST-allowlist parser security fix and callable-bound execution grants); post-3.0.1 commits on main (through 0cd5e56) add versioned evidence identities and the opt-in SQLite EffectStore. The source and CI evidence below refer to pre-3.0 commit 963977e. Package maturity is Beta; individual adapters (13 on PyPI) have their own stability labels.

963977e63b51

Passed

Selected CI checks passed

The inspected head passed Python 3.10-3.13 tests, package checks, docs checks, and governance regression gates. Main CI excludes slow, benchmark, and end-to-end tests.

Inspect CI evidence

Multi-agent coordination

ACGS Swarm

Mixed maturity · optional research

Release and source

1.1.0 is inspected source metadata. Current package publication was not independently verified. The project separates its core API, advanced integrations, and research modules.

f40af8dea690

Needs attention

CI needs attention

Default Python 3.11/3.12 tests, type checks, and package checks passed. Overall CI failed when one PostgreSQL authority-store outbox test timed out.

Inspect CI evidence

Self-hosted HTTP service

Enhanced Agent Bus

Evaluation · operational setup required

Release and source

3.0.2 is inspected source metadata. No GitHub releases were returned in this audit; current PyPI publication was not independently verified.

e4ecaf56b31a

Passed

Selected CI checks passed

The inspected head has a green CI run covering selected smoke, regression, conformance, and critical-path suites. It is not a run of every repository test or proof of production operation.

Inspect CI evidence

Infrastructure policy companion

CFT Governance Pack

Early source companion

Release and source

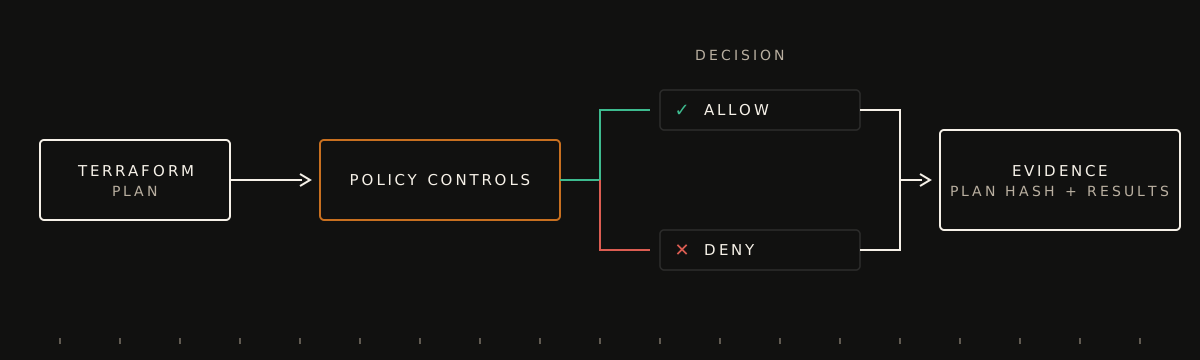
An early companion pack in the ACGS monorepo. This audit verified source and example workflows, not a managed service or independently published package.

Not observed

No exact-head CFT run observed

The repository contains CFT tests and a path-filtered workflow. No CFT run appeared in the 12 workflow runs returned for the inspected monorepo head. No package tests were rerun for this review.

CLAIM BOUNDARIES

Keep the evidence in context.

Integrated paths define coverage

Installing a package does not mediate every action. A kernel receipt check, a Lite validation result, a peer vote, and a bus acceptance response are different contracts.

Source versions are not releases

gove-zone’s PyPI artifact (1.0.0rc2) and ACGS-Lite’s PyPI release (3.0.1) and GitHub release history are published artifacts; 13 framework adapters, enhanced-agent-bus (3.0.2), clinicalguard (1.0.1), and constitutional-swarm (0.1.1) also have PyPI distributions tracked alongside the inspected source commits.

Tests have a defined scope

Green selected checks do not establish production readiness. Failed or missing runs are shown above. No uptime, latency, customer-count, or current benchmark claim is made.

Mappings are not certificates

Policy outcomes and control mappings do not establish certification or regulatory approval. Identity, storage, operations, and deployment evidence need separate review.

Put one real workflow under your control.

Choose one tool. Define what it may do. Inspect what happens when a request crosses the boundary.