Review the project baseline
Rules evaluate project labels, folder placement, billing, and APIs without modifying the upstream Terraform modules.
INFRASTRUCTURE POLICY COMPANION
Evaluate Google Cloud Foundation Toolkit Terraform plans against YAML controls. Produce a decision and evidence bundle that your CI workflow can inspect before an apply step.
For platform engineers evaluating Google Cloud infrastructure changes.
WHERE IT FITS
Use this to attach configurable plan checks to a CI pipeline. Your pipeline must enforce the result before a deployment can proceed.
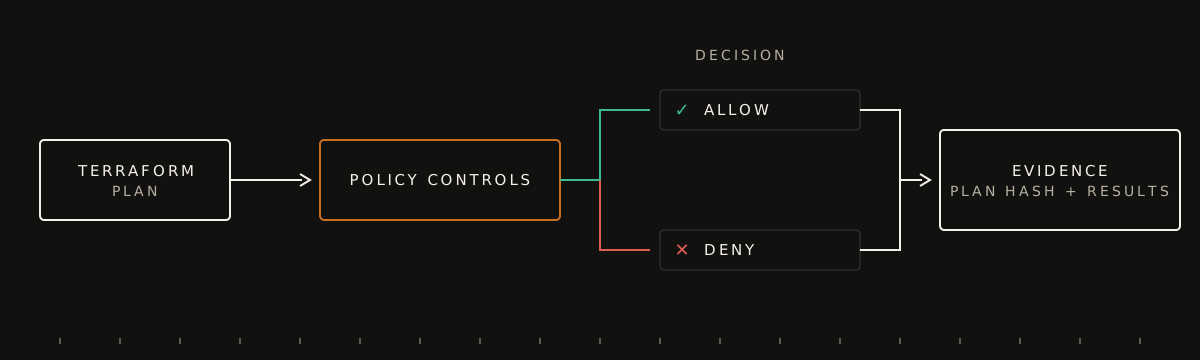
Supply Terraform plan JSON for the proposed Google Cloud change.
Run the configured YAML rules over the plan’s resource changes.
Inspect the JSONL evidence and denial exit code before your apply job.
INSIDE THE PRODUCT
Follow each behavior to its implementation or maintained documentation.
Rules evaluate project labels, folder placement, billing, and APIs without modifying the upstream Terraform modules.
Implemented controls cover selected IAM roles, service-account keys, exposed SSH/RDP, firewall logging, and subnet flow logs.
The pack checks private nodes, Workload Identity, Shielded Nodes, and release-channel settings represented in the plan.
JSONL output contains the plan hash, supplied actor and role, control results, timestamp, and Merkle root. The CLI exits with code 2 on denial.
LOCAL EVALUATION
The CFT Governance Pack is not published as a package. Request evaluation access at evaluation@acgs.ai. The example evaluates a local allowed-plan fixture; it does not call terraform apply.
Use Python 3.10+ and the evaluation package provided on request.
Run the fixture against the bundled policies and choose a local output path.
Review the example workflow and implement the apply dependency in your own pipeline. Configure Google Cloud policy validation separately.
# The CFT Governance Pack is not published as a package.
# Request evaluation access at evaluation@acgs.ai.
The output is a local evidence file. The supplied actor and role are metadata, not authenticated identities.
Copy the example or select the code manually.
DESIGN AROUND THE BOUNDARY
The integration and operating conditions are part of the product decision.
No. The supplied GitHub Actions YAML is an attachment example and does not run terraform apply. Its gcloud beta terraform vet step is an echo placeholder that prints setup guidance; configure that integration yourself.
It covers the implemented rule kinds and the data present in the Terraform plan. It complements Google Cloud policy validation and needs controls appropriate to your environment.
No. The writer creates a JSONL file at the chosen path. Retention, access control, external anchoring, and CI identity assurance are responsibilities of the integrating system.
It records the outcome of configured checks on a plan. It does not establish deployed state, regulatory compliance, or independent assurance.
SOURCE, RELEASE, AND CHECKS
An early companion pack in the ACGS monorepo. This audit verified source and example workflows, not a managed service or independently published package.
Reviewed 2026-09-08. Source version and published release are tracked separately.
The repository contains CFT tests and a path-filtered workflow. No CFT run appeared in the 12 workflow runs returned for the inspected monorepo head. No package tests were rerun for this review.
FROM READING TO EVALUATION
Follow one example. Inspect the result. Decide whether it fits your workflow.